This type of phishing attack can be ridiculously sneaky
We love when our customers run red team engagements. Aside from testing and validating current security controls, detections, and response capabilities, we see it as a great opportunity to partner with our customers on areas of improvement. Here’s the story of how a red team helped Expel improve our phishing service and how we used our platform capabilities to detect some sneaky activity.
So, what happened? (Spoiler alert: it’s a homoglyph attack)
Our client—let’s call them Acme Corp—had an enterprising red teamer with a clever idea. For one of their exercises, the red team purchased a domain: ạcmehome[.]com. Notice anything odd? Let’s look closer:
ạcmehome[.]com vs acmehome[.]com
If you missed it, don’t feel bad. That’s the point.
A bit of background
A homoglyph attack registers a domain that looks identical to a legitimate one by swapping in a character from a different script. Unicode contains thousands of characters that render nearly identically to Latin letters—a Cyrillic “а” (U+0430) is a different character from a Latin “a” (U+0061), but on screen they’re the same shape. Internationalized domain names allow those characters in URLs, so an attacker can register a domain that is byte-for-byte different from yours and visually indistinguishable from it.
That’s the whole trick. There’s no exploit, no malware, no clever payload—just a character your eye can’t tell apart from another one, sitting in a URL your user is about to click.
| Character | Code point | Looks like | Script |
|---|---|---|---|
| a | U+0430 | a (U+0061) | Cyrillic |
| e | U+0435 | e (U+0065) | Cyrillic |
| o | U+043E | o (U+006F) | Cyrillic |
| p | U+0440 | p (U+0070) | Cyrillic |
| c | U+0441 | c (U+0063) | Cyrillic |
| y | U+0443 | y (U+0079) | Cyrillic |
| x | U+0445 | x (U+0078) | Cyrillic |
| i | U+0456 | i (U+0069) | Cyrillic |
| s | U+0455 | s (U+0073) | Cyrillic |
| o | U+03BF | o (U+006F) | Greek |
| ɑ | U+0251 | a (U+0061) | Latin (IPA) |
| ạ | U+1EA1 | a (U+0061) | Latin (Vietnamese) |
This is partial list. Unicode contains many more—these are among the most commonly abused in domain spoofing. Also, not every lookalike attack uses Unicode at all. Substituting rn for m, or a capital I for a lowercase l, works with pure ASCII and defeats any filter that only checks for non-ASCII characters.
We love when our customers run red team engagements. Aside from testing and validating current security controls, detections, and response capabilities, we see it as a great opportunity to partner with our customers on areas of improvement. Here’s the story of how a red team helped Expel improve our phishing service and how we used our platform capabilities to detect some sneaky activity.
There are lots of homoglyphs and the potential for mischief is off the hook (which is why top-level domain registries and browser designers are exploring ways to minimize the risks of hõmògIÿphìč chäôs).
There’s even a homoglyph “attack geñerator. This app is meant to make it easier to generate homographs based on homoglyphs than having to search for a look-a-like character in Unicode, then copying and pasting. Please use only for legitimate pen-test purposes and user awareness training.
Back to Acme. The red team’s fake domain used the Vietnamese homoglyph to trick users into thinking it’s the actual domain—in this case, acmehome[.]com—when that itty-bitty dot under the “a” makes a huge difference. The tactic also relies on a security operations center (SOC) analyst who’s been staring at mind-numbing alerts slipping up and not noticing the difference in domain names. In truth, for most SOCs and attackers, this isn’t a bad strategy.
What we did
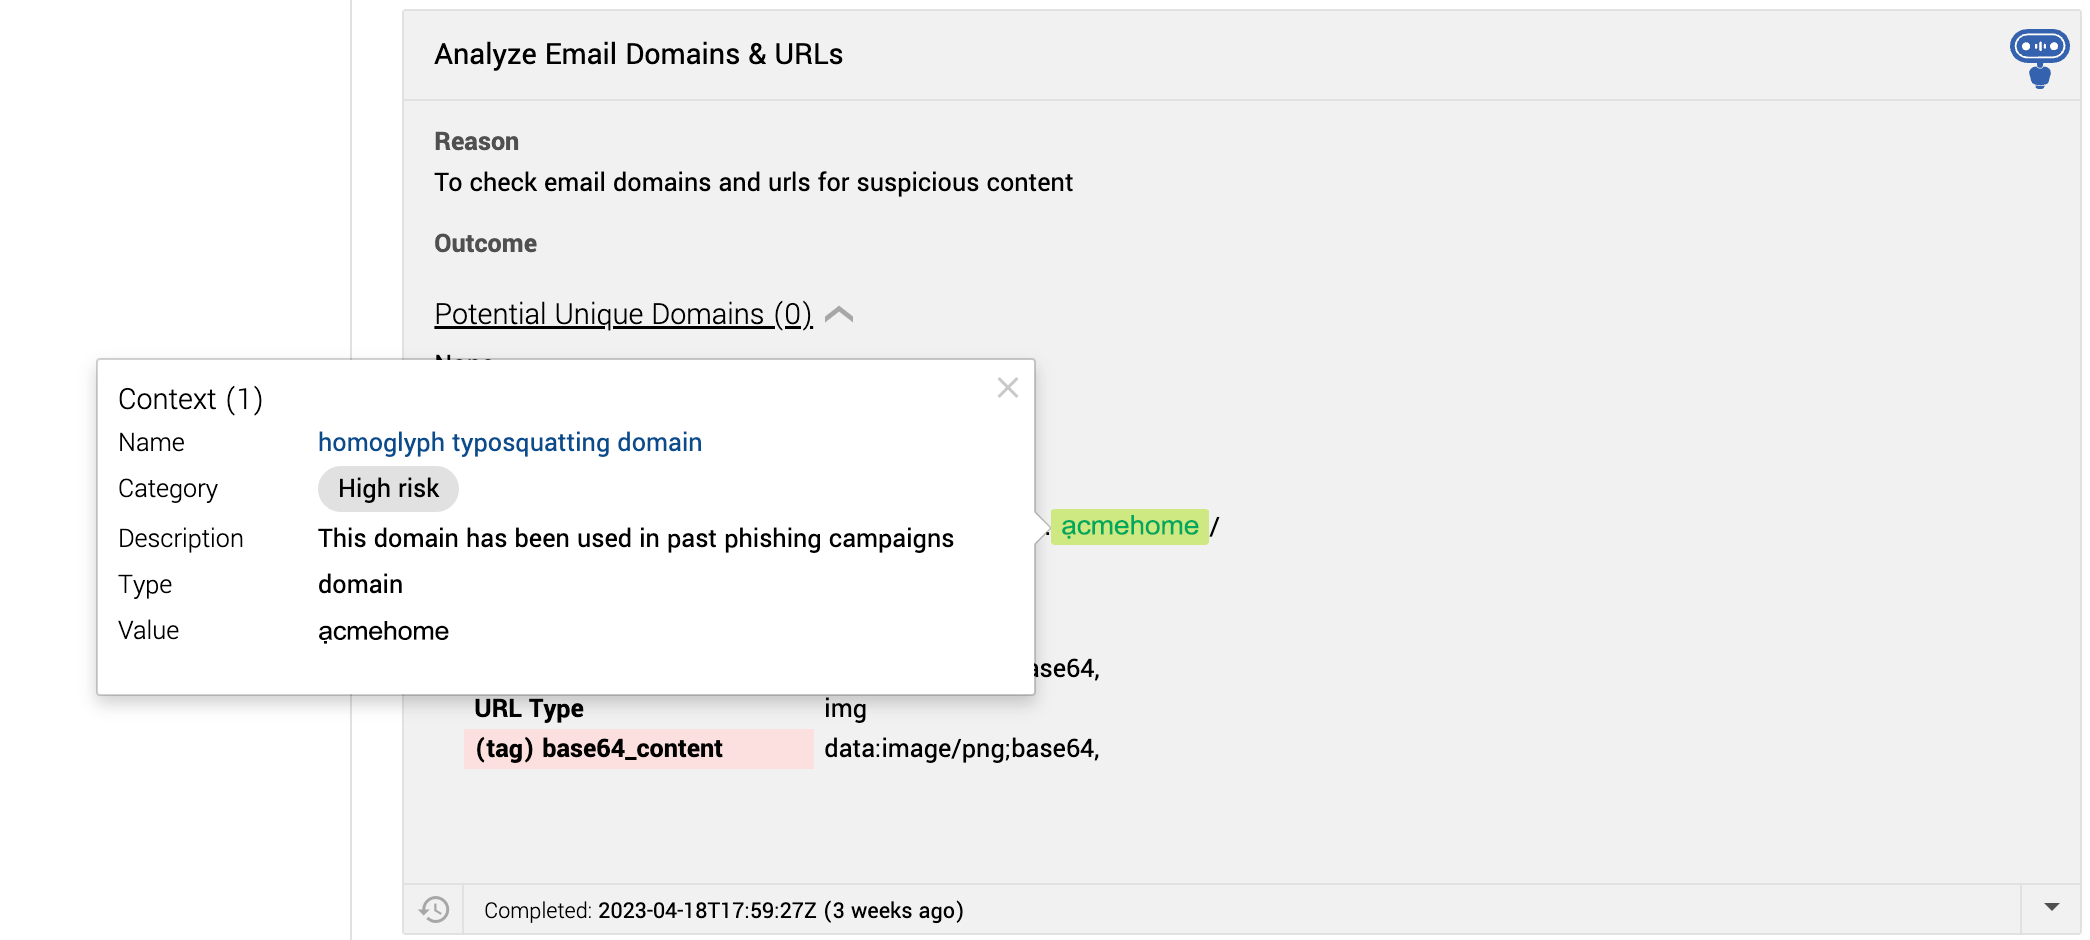
After meeting with the red teamers, we uncovered a need to better scrutinize unique domains within emails that could intentionally trick the naked eye. Technology to the rescue. Since we have a content-driven platform capability—customer context (CCTX)—Expel was easily able to change the platform behavior to recognize the attack for that homoglyph site in Acme’s Workbench™. Having a platform that’s content-driven means Expel users can change how the platform operates without having to engage with engineering teams to release new features.
NOTE: When you have a platform that allows users to drive content and configuration, it means that once you understand how a feature works, you can bring your own creativity to solving problems. It’s really fun when you’re able to adapt a feature (especially if it allows for rapid response to new or emerging techniques) to accomplish something unanticipated during the design of the feature—which is what happened in this case.
The result?
Acme Corp’s red team conducted a similar attack again, and this time the SOC caught it with CCTX.
How to defend against homoglyph attacks
- Normalize and compare. Convert domains in inbound email to Punycode and flag any that don’t round-trip to pure ASCII. A domain rendering as
acmehome.comthat encodes toxn--something is worth a look. - Score visual similarity, not just string equality. Exact-match blocklists miss homoglyphs by design. Compare candidate domains against your own and your partners’ using a similarity measure that accounts for lookalike characters.
- Watch newly registered domains. Homoglyph domains are usually bought shortly before use. Domain age is one of the stronger signals available.
- Check your browser and email client behavior. Some clients display the Unicode form, some display Punycode, and the difference determines whether a user sees
xn--cmehome-4r0d.comor something that looks exactly like your domain. - Register the obvious variants of your own domain. Cheaper than the incident.
- Don’t rely on analysts spotting it. This is the honest one. An analyst several hours into an alert queue will not notice a dot under an “a,” and building a process that assumes otherwise is building a process that fails.
What does it all mean?
Multiple things, possibly.
- Homoglyphs are a technique SOCs need to account for. Not an exotic one—a red teamer pulled it off with a domain purchase.
- There are branding reasons to care, not just security ones. Most businesses with accented names—Société Générale, A.P. Møller-Mærsk, Nestlé—use unaccented letters in their URLs. But if the accented URL does work (loréal.com, say), what stops an attacker from swapping in a different accent? è instead of é.
- It matters more for companies in non-English-speaking countries, whose languages use extended iconography as a matter of course. Which means it matters more for the cybersecurity firms serving them. Like us.
If you have questions, or think your organization might be at risk, drop us a line.