Cybersecurity blog
Product
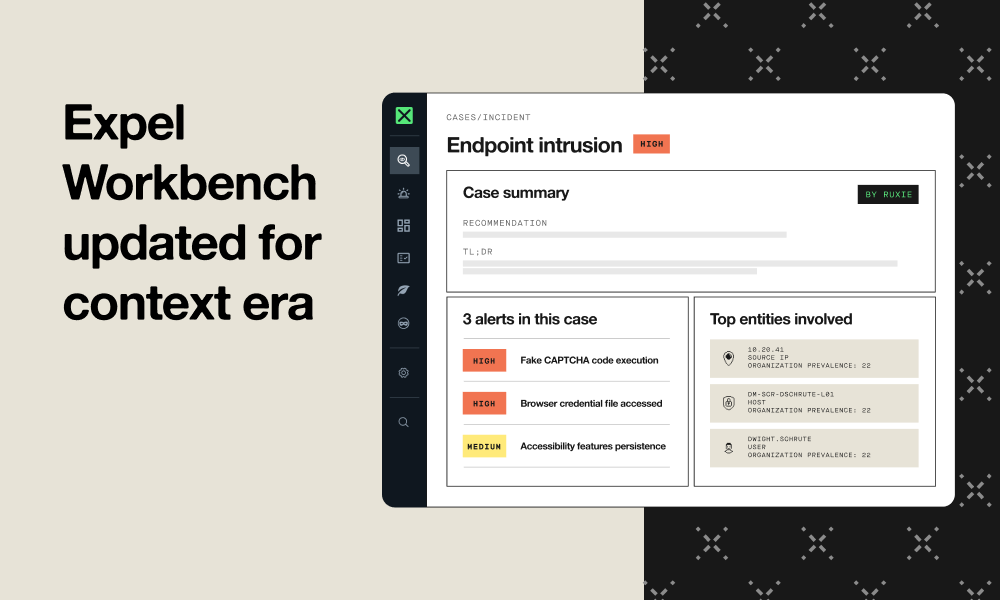
Why solving for context-driven security required rebuilding everything from the ground upExpel rebuilt Workbench around context, not alerts. See what’s new and what's next: Cases view, Ruxie triage agents, workflow builder, and an MCP.
Rapid response | 3 min read
How Expel is protecting you from ARTEX and AI-driven attack frameworksAI attack frameworks like ARTEX speed up intrusions, but attackers still have to sign in, move around, and touch data. Here's how Expel detects them.
MDR | 5 min read
We’re building tomorrow’s legacy software todayVulnpocalypse is a misnomer for a context and code problem. We're writing tomorrow's legacy software today, and need to plan accordingly.
Product | 6 min read
Why solving for context-driven security required rebuilding everything from the ground upExpel rebuilt Workbench around context, not alerts. See what’s new and what's next: Cases view, Ruxie triage agents, workflow builder, and an MCP.
Threat intel | 4 min read
What’s in a name? The story behind SynkLoaderWho names malware, and how? Find out how SynkLoader got its name and why Expel won't turn threat actors into comic book villains.
Threat intel | 2 min read
Consent phishing skips the password and walks in the front doorExpel's SOC has seen a spike in consent phishing lately, so here's what you need to know on how to defend against it.
MDR | 6 min read
Why context is the new heart of the OSCAR methodologyManual collection can’t keep up with machine-speed attacks. See how swapping collect for contextualize turns the OSCAR methodology into a continuous loop.
Product | 2 min read
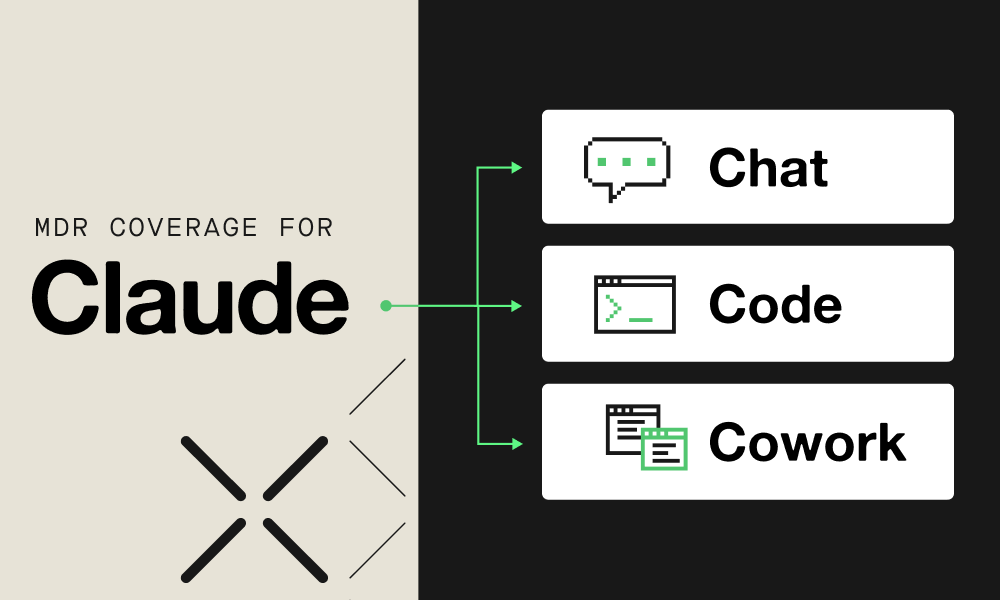
Expel MDR now covers Claude Chat, Code, and CoworkExpel Managed Detection and Response (MDR) now covers Claude Chat, with Claude Code and Claude Cowork in early access. Here's what we monitor.
Current events | 4 min read
[un]prompted II: Six months is a long timeThe model can't be your security control; it has to be the harness around it. Defenders must build and test theirs seriously, starting with what agents can reach.
Security operations | 6 min read
Pen test vs. BAS vs. red team vs. tabletop: What does your team need?Breach and attack simulation vs. penetration testing vs. red teaming vs. tabletops: what each one tests, what it costs, and the order to run them in.
Company news | 6 min read
The AI poverty line: What it means for security teamsExpel CTO Greg Notch on the AI poverty line—the divide between security teams that can wield AI and those that can't, and how to land above it.
Product | 2 min read
What we built: October 2026In October, Expel launched two new Microsoft Entra ID threat hunts, and a more accurate Alert Analysis dashboard.
Rapid response | 8 min read
Fake Claude Code extensions in Cursor: Malicious activity after the exposure windowA fake Claude Code extension in Cursor’s marketplace planted SSH backdoors on developer machines. See what Expel found and how to check every machine.