OT Security
OT security with the tools you already use
Attackers reach your operations through the same doors your team uses: VPNs, identities, and Windows. Expel watches those doors for you, 24x7.
OUR DIFFERENCE
OT security monitoring without OT tools
We cover the way in with the tools you already run, move fast on your IT, and stop clean at the physical perimeter.

No new tools required
If a system runs an EDR agent, sits behind a network sensor, or has a login, we can watch it. We read the alerts your tools already send.

Efficient case management
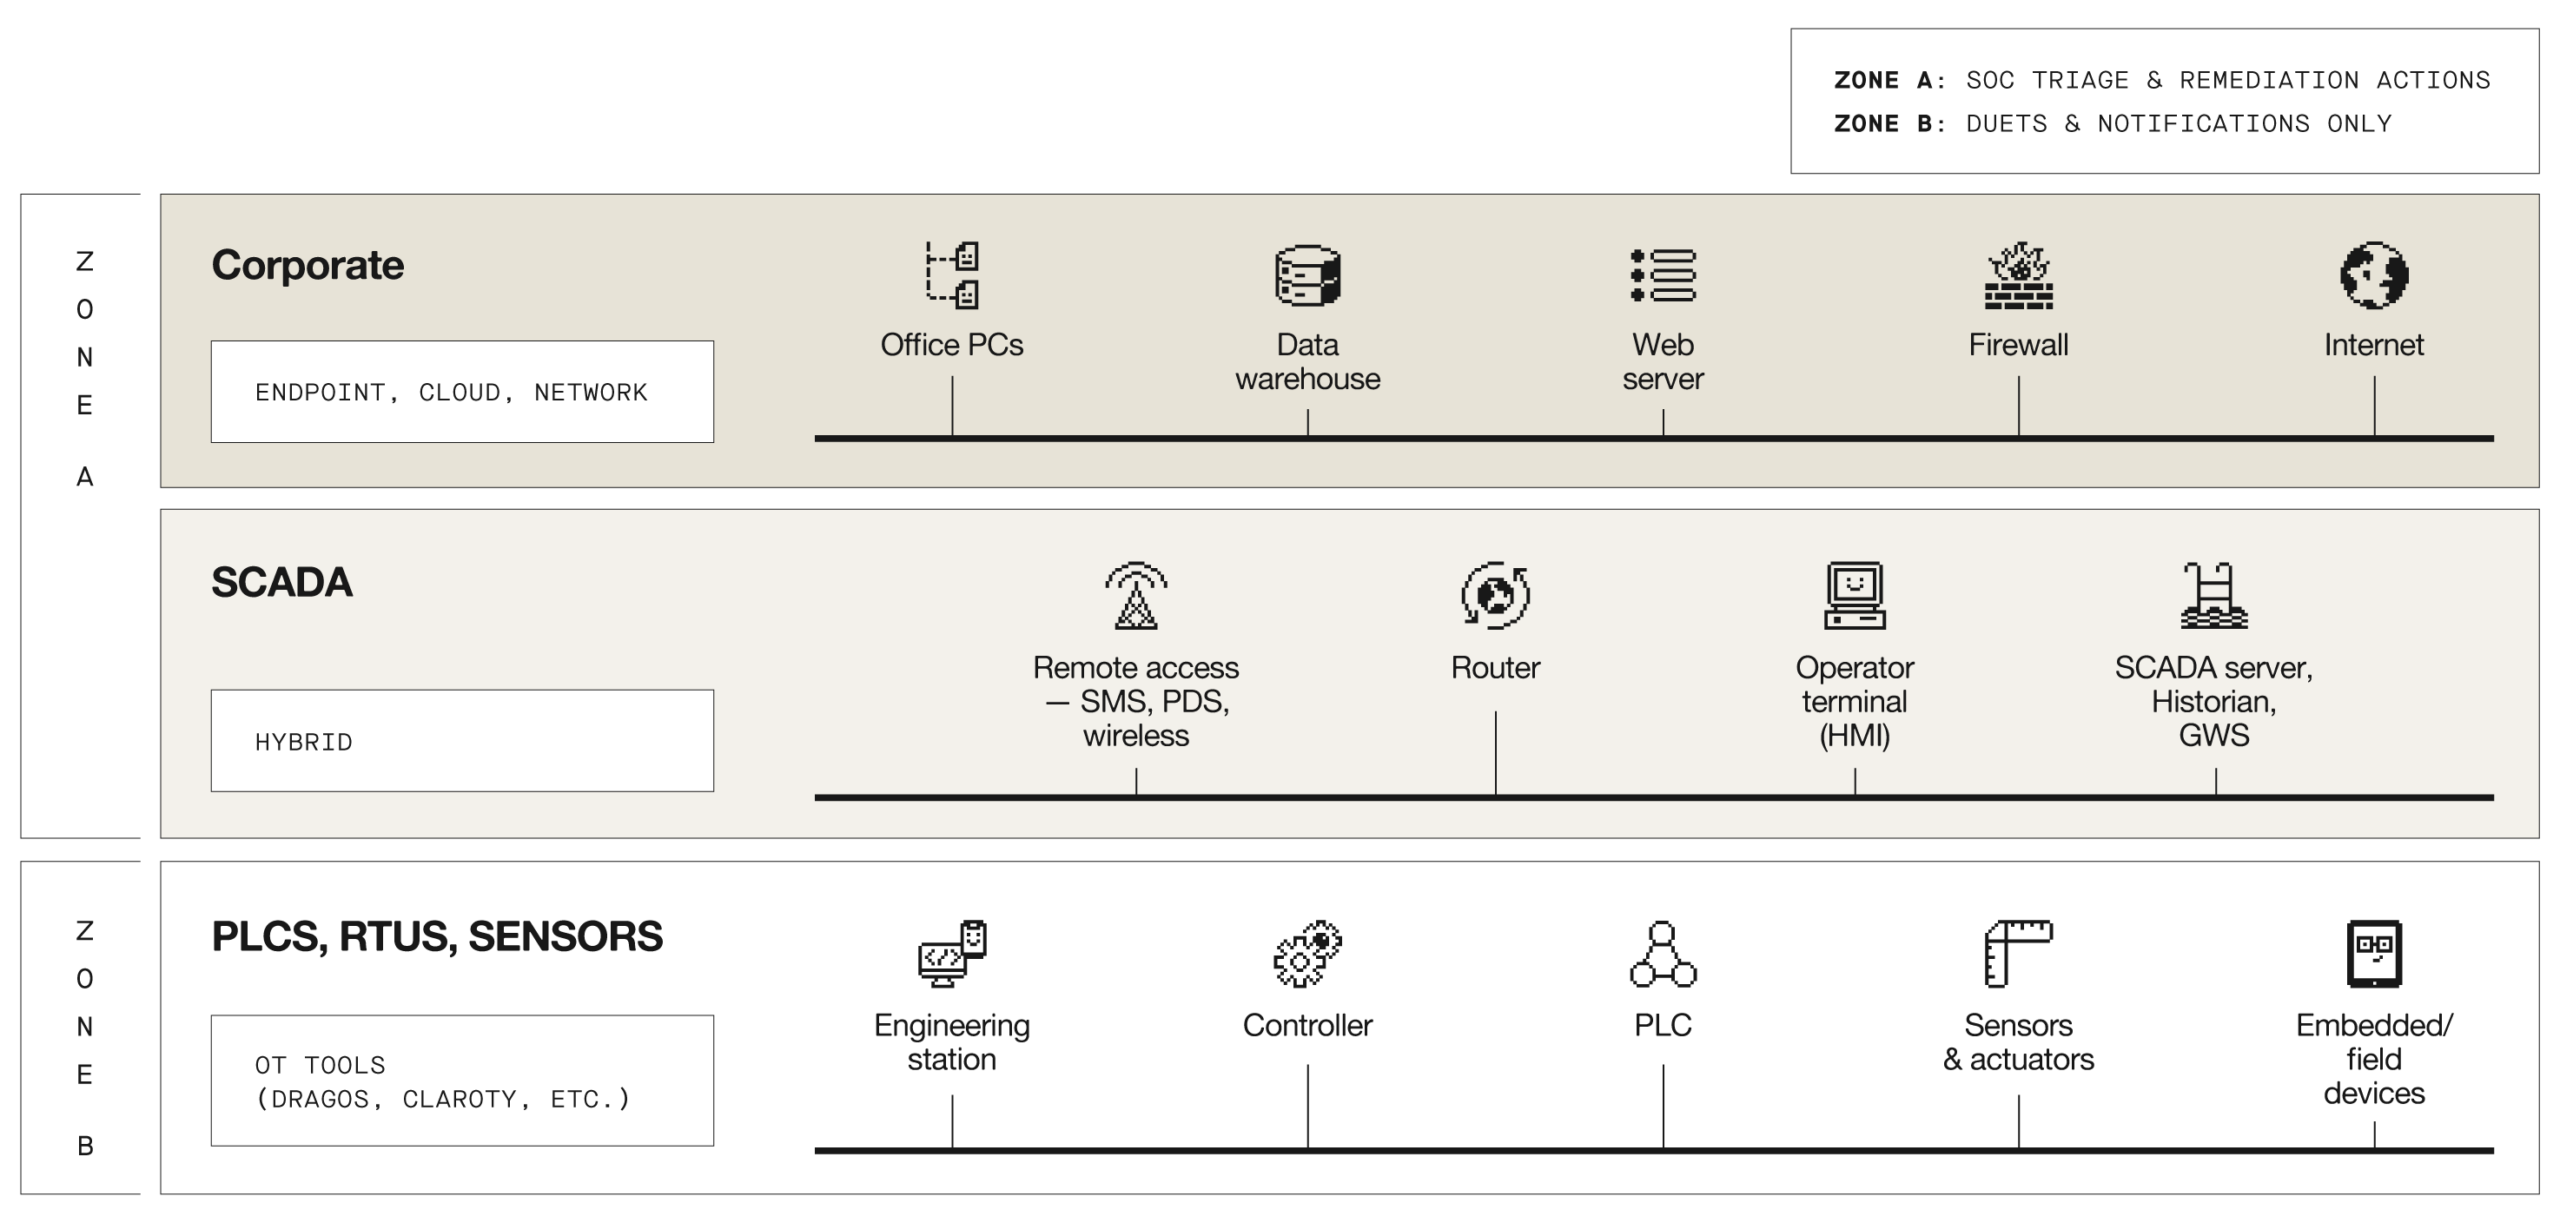
One attacker, one case, tracked across all three layers at once—not three alerts stuck in three queues.

Honest about the boundary
We watch the path up to the edge of your OT, then hand off. Controllers and safety systems stay with your engineers. No risky remote guesses.
HOW IT WORKS
One intrusion, tracked wherever it goes
AI risk shows up on three fronts—attackers using AI against you, employees feeding data to public models, and the AI systems you’re building—and these signals correlate with data points across the rest of your environment. It’s the same trusted MDR service, same platform, and outcomes you can see. Our threat hunters are also looking for AI risk proactively, so you get ongoing coverage without having to hire in-house experts.
More than monitoring
Why Expel
Everything that makes Expel work on your other attack surfaces works here too: a real SOC, full context, hunting, and people who own the outcome.

A real SOC, and a clean handoff
Our SOC runs 24×7 and knows how IT intrusions climb into OT. When it’s time to hand off, your engineers get the full picture.

You see what we see
You see the same evidence and reasoning we do. That’s critical when a containment call could stop the line.

Hunting for what doesn’t alert
Living-off-the-land intruders can sit in critical infrastructure for months with no alert. Our hunters go find them by hand.

Built for how OT gets hit
Tuned to how industrial intrusions run: VPN credential abuse, ransomware crews hitting manufacturers. Updated as they shift.
Actually helpful resources
Annual Threat Report 2026
Expel’s latest threat intelligence report takes real-life cybersecurity lessons learned and transforms them into actionable insights for security operators.
Gartner® Market Guide for Managed Detection and Response
Download the latest Gartner® Market Guide for MDR Services for help navigating the complexities of the MDR marketspace.
A security leader’s guide to deploying AI in a SOC
AI automation in the SOC starts with trust. Expel's Trust vs. Impact framework maps which SOC workflows to automate first, built on 10 years of practice.
Catch it while it's still an IT problem
See our operators trace a real intrusion towards OT and shut it down before it crosses the line.