Cryptojacking is the unauthorized use of someone else’s computing resources to mine cryptocurrency, often without the victim’s knowledge. It can degrade system performance, increase cloud costs, and signal a broader compromise of the environment.
A cryptojacking attack can be pretty straightforward–since there is no need to escalate privileges or move laterally to get to the host with the secret they need. In 2024, our Annual Threat Report indicated cryptojacking made up more than a quarter of all attempts to deploy malware. It’s a sweet gig for the bad guys, too: after the miner is deployed, they can sit back, relax, and watch the money pile up. Cryptojacking continues to be a common threat in 2026.
Are cryptojacking attacks a cyber threat?
Cybercriminals are always looking for new ways to make money. We often hear about holding data or systems for ransom. But what about cryptojacking? It’s when a threat actor steals your organization’s computing resources/power and uses it to mine various crypto-currency blockchains. The bad news: it can slow your network way down, and even shut down critical processes.
How does cryptojacking work?
How do they get in? Public application exploitation. Access key compromise. Phishing emails. USB devices. Cryptojacking typically involves two main methods of attack, but the list grows every year.
- Malicious websites or ads: Cybercriminals inject cryptomining scripts into websites or online ads. When users visit these compromised sites or interact with infected ads, the script automatically runs in the background, using the visitor’s processing power to mine cryptocurrency.
- Malware infection: Hackers can also infect devices with malware specifically designed to mine cryptocurrency. This malware often spreads through phishing emails, malicious downloads, or unsecured networks.
In recent years, threat actors have launched numerous campaigns to breach poorly secured Kubernetes clusters and hijack their underlying cloud resources for cryptomining. Such attacks are designed for persistence. They can significantly degrade performance, increase energy consumption and cost, strain hardware resources, and provide a gateway for future attacks
In all cases, the mining activity happens without the user’s permission. This often makes the device work incorrectly as it uses more energy, and shortens its lifespan.
Expel’s 2026 Annual Threat Report
Our SOC sees millions of alerts yearly. Here’s what attackers are actually doing—and how to play defense when you’re short on time and people.
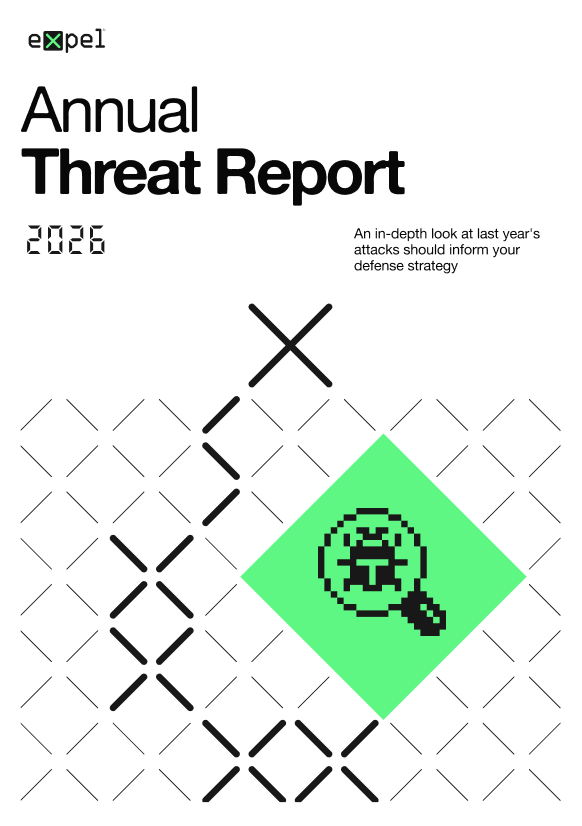
What does a cryptojacking attack chain look like?
Cryptojacking is a short chain. There’s no data to steal and no ransom to negotiate, so bad actors skip most of the steps you’d see in a ransomware intrusion. They get in, drop a miner, hide it, and collect.
Cryptojacking attack chain: initial access, execution, evasion and persistence, mining, monetize and expand
1. Initial access. The usual entry points are exposed management interfaces (Docker APIs, Kubernetes kubelets, Redis), leaked or stolen cloud access keys, vulnerable public-facing apps, and phishing. Cloud environments are a favorite because the victim pays the compute bill.
2. Execution. A script or container pulls the miner from attacker-controlled infrastructure. XMRig is the most common payload.
3. Evasion and persistence. The miner needs to run for weeks, not hours. Bad actors add cron jobs or services, kill competing miners, rename processes, and cap CPU use so the spike doesn’t trip basic alerts. CyberArk documented an attacker doing exactly that after reaching an unprotected Kubernetes console.
4. Mining. The miner connects to a mining pool and starts burning your CPU, GPU, or cloud spend.
5. Monetize and expand. The attacker collects the coins. Many also harvest credentials from the host and spread to more systems, which is why a miner is often a sign of a bigger problem.
MITRE ATT&CK tracks this behavior as T1496.001, Resource Hijacking: Compute Hijacking.
Browser-based vs. host-based cryptojacking
Not all cryptojacking works the same way. The two main types differ in where the miner runs, how long it lasts, and what you do about it.
| Browser-based | Host-based | |
|---|---|---|
|
Where it runs |
In the visitor’s browser tab | On the endpoint, server, container, or cloud instance |
|
Delivery |
JavaScript on a compromised site or in an ad | Malware, scripts, or containers deployed after initial access |
|
Persistence |
Stops when the tab closes | Survives reboots through cron jobs, services, or scheduled tasks |
|
Typical payload |
JavaScript or WebAssembly miner (Coinhive was the best-known example) | Compiled miner, usually XMRig, plus a loader script |
|
Scale of theft |
Small per victim, depends on volume of visitors | Large, especially on cloud and container infrastructure |
|
Who pays |
Site visitors (battery, performance) | The organization (cloud bills, hardware, downtime) |
|
Signal of a bigger breach |
Rarely | CPU and cloud-spend anomalies, process and network telemetry, cloud audit logs |
|
Detection |
Browser or network filtering of known mining scripts | Often—the attacker already has access |
|
Prevention |
Script and ad blockers, DNS filtering | Patching, closing exposed APIs, credential hygiene, endpoint and cloud monitoring |
|
Status today |
Faded after Coinhive shut down | The main threat |
Browser-based mining made headlines in 2017 and 2018, but host-based mining is the bigger problem for security teams now. It lasts longer, scales better, and usually means someone got into your environment.
Cryptojacking malware families and campaigns
A few names show up again and again in cryptojacking incidents.
XMRig
XMRig is an open-source miner for Monero and other coins that use the RandomX algorithm. It’s legitimate software. That’s the problem. It’s free, fast, and easy to configure, so it’s one of the most commonly abused tools in host-based cryptojacking. MITRE lists XMRig use by groups including TeamTNT and Blue Mockingbird. Because XMRig is a real tool, antivirus signatures alone won’t catch every deployment. Attackers recompile it, rename it, and wrap it in custom loaders.
Coinhive
Coinhive was a JavaScript miner that let site owners earn Monero from visitor CPU. Criminals quickly figured out they could inject the script into sites they didn’t own, and it became the face of browser-based cryptojacking. Coinhive shut down on March 8, 2019, citing a drop in hash rate after a Monero hard fork and a steep fall in Monero’s value. Copycat scripts still pop up, but nothing has matched its reach.
TeamTNT
TeamTNT is a cybercriminal group known for targeting cloud and container environments. Two campaigns show how they work:
- Hildegard (2021): Unit 42 researchers found this Kubernetes-focused malware searching for kubelet APIs with anonymous access, then deploying miners across as many pods as possible.
- Chimaera (2021): AT&T Alien Labs traced this multi-platform campaign to July 2021. It hit Windows, Linux, AWS, Docker, and Kubernetes with a miner, an IRC bot, and credential-stealing scripts.
TeamTNT is also known for stealing AWS credentials. The miner is the visible part. The stolen keys are the lasting damage.
What this looks like in our SOC
Expel’s SOC investigated a coin-mining intrusion in a customer’s AWS account. The attacker used a compromised root IAM access key to enumerate the environment and launch 10 c5.4xlarge EC2 instances to mine Monero. No malware on a laptop, no phishing email in sight—just a leaked key and someone else’s cloud bill. In Q2 2026, unauthorized access to cloud environments made up 48.4% of cloud incidents our SOC investigated, often ending in cryptominer deployments.
What are the signs of cryptojacking?
Since cryptojacking doesn’t typically involve overt disruption like ransomware, it can be difficult to detect.
However, there are several red flags to watch for:
- Slower performance: devices or networks may become noticeably sluggish, with increased lag times or crashes.
- Overheating: The use of CPU or GPU resources can cause devices to overheat, leading to hardware malfunctions or failure.
- Increased energy use: mining cryptocurrency demands significant processing power, which can result in higher-than-usual electricity bills.
- Unexplained CPU usage: a sudden spike in CPU or GPU usage, especially when no resource-heavy applications are running, can indicate cryptojacking.
What impact does cryptojacking have on organizations?
For businesses, cryptojacking attacks can have serious consequences beyond just performance issues. Widespread cryptojacking can:
- Increase operational costs: the drain on energy and resources from these types of attacks can result in higher costs.
- Reduce productivity: slowed networks and devices hinder productivity, affecting daily operations.
- Shorten hardware lifespan: the excessive load on systems can lead to premature hardware failures, resulting in costly repairs or replacements.
- Increase security risks: cryptojacking infections may open the door to other vulnerabilities or indicate a broader breach of system security.
How do you prevent cryptojacking?
Fortunately, attacker entry points for cryptojacking overlap with those for other threat types like ransomware, so focused efforts to reduce your cryptojacking attack surface can help protect against multiple problems.
Cryptojacking prevention strategies
Cryptojacking prevention requires a multi-layered security approach, focusing on both personal devices and organizational networks. Here are some key steps:
- Install anti-malware software: use reputable anti-malware solutions to detect and block cryptomining scripts and malware.
- Update software regularly: keep operating systems, browsers, and software up-to-date to patch vulnerabilities that hackers may exploit.
- Use browser extensions: extensions like NoCoin and MinerBlock can block cryptojacking scripts from running on websites.
- Monitor system performance: regularly monitor CPU and GPU usage to detect unusual spikes that may indicate mining activity.
- Educate employees: if you’re an organization, ensure employees are aware of phishing schemes and how to avoid suspicious links or downloads.
Frequently asked questions
How does cryptojacking work?
Cryptojacking attackers gain access through common vectors—phishing, application exploitation, or compromised credentials—then deploy cryptomining scripts or malware that run silently in the background. Some attacks target individual devices via malicious websites or ads; others compromise cloud infrastructure like Kubernetes clusters for large-scale mining. In every case, the victim’s computing resources do the work while the attacker collects the cryptocurrency.
What are the signs of a cryptojacking attack?
Cryptojacking is designed to stay hidden, but it leaves behind resource-drain indicators. The most common signs are unexplained spikes in CPU or GPU usage, noticeable slowdowns in device or network performance, devices running hotter than usual, and unexpected increases in energy costs. Because these symptoms can resemble other performance issues, organizations should monitor system resource usage continuously so anomalies get flagged rather than dismissed.
What impact does cryptojacking have on organizations?
Beyond the performance hit, cryptojacking drives up operational costs through higher energy consumption and accelerated hardware wear. It also reduces productivity across the organization and—critically—can signal a deeper security problem. Attackers who have deployed a cryptominer have already achieved persistent access, meaning the same foothold could be used to stage ransomware, data theft, or other more disruptive attacks.
How do you prevent cryptojacking?
Cryptojacking prevention relies on the same layered security approach used to defend against other malware. That means keeping software patched, deploying anti-malware tooling, monitoring for anomalous CPU and GPU usage, and training employees to recognize phishing attempts. Browser extensions that block cryptomining scripts add an additional layer of protection for endpoint users. Because cryptojacking entry points overlap heavily with ransomware, investments in this area pay dividends across multiple threat types.
What is the difference between browser-based and host-based cryptojacking?
Browser-based cryptojacking runs a JavaScript miner inside a visitor’s browser tab and stops when the tab closes. Host-based cryptojacking installs a miner on an endpoint, server, container, or cloud instance and keeps running until someone finds it. Host-based attacks are the bigger problem today because they last longer, scale further, and often mean the attacker already has access to your environment.
What are examples of cryptojacking malware?
XMRig, an open-source Monero miner, is the most common payload in host-based attacks. Coinhive was the best-known browser-based miner before it shut down in March 2019. TeamTNT’s Hildegard and Chimaera campaigns are well-documented examples of cryptominers deployed against Kubernetes, Docker, and cloud environment