Cybersecurity blog
Threat intel
SynkLoader: when you throw in everything but the kitchen sinkDiscover a new malware family, SynkLoader. See how we reverse-engineered its phishing tactics to expose its attack chain.
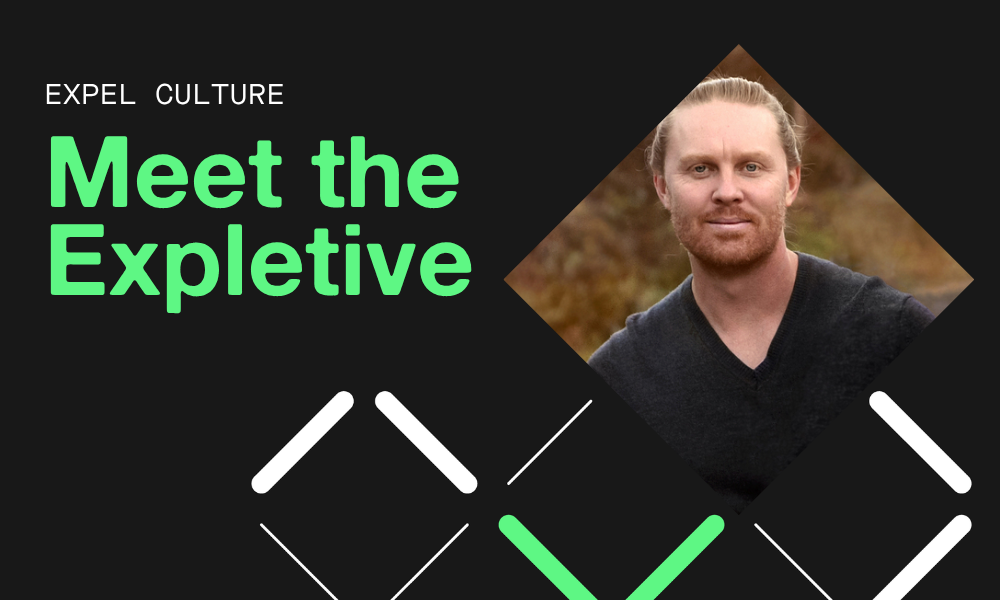
Expel culture | 4 min read
Meet the Expletive: Todd Bane, Director of Professional ServicesMeet Todd Bane, Director of Professional Services at Expel. He came up through bank IT and the Pentagon, and he restores tractors.
Product | 3 min read
New Ruxie AI power-up: Precedent engine turns repetitive alerts into faster decisionsRuxie's precedent engine feature is a long-term memory for Expel's SOC, using AI to instantly recognize when a new alert matches previous historical cases.
Threat intel | 3 min read
Patch Tuesday: September 2026 (Expel’s version)September's Patch Tuesday is Microsoft's biggest ever at 964 CVEs, with two exploited zero-days. Plus a critical Adobe Commerce flaw that can't wait.
Product | 2 min read
What we built: August 2026This month we released MDR for AI—coverage for the AI attack surface—along with CSV exports and a new home for product documentation.
MDR | 4 min read
Shadow AI risk: The 4 behaviors that create real exposureShadow AI risk comes down to how employees use AI. Get the four real risk categories and a practical governance approach.
MDR | 5 min read
Five questions your board will ask about AI riskBoards are asking about AI risk now. Get 5 real questions CISOs face and a simple framework for answering each one with confidence.
Threat intel | 16 min read
The AI CVE exploitation evidence story: Headlines are scarier than realityExpel's vulnerability intel team is currently monitoring 1,250+ CVEs related to 50 unique AI vendors; here's what we think you should know.
MDR | 5 min read
Mapping AI detections to MITRE ATLAS: How Expel does itSee how Expel MDR for AI labels AI-related detections against MITRE ATLAS tactics in Workbench, with a real mapping walkthrough.
Product | 4 min read
New Ruxie AI power-up: Meet rapid triage agent, the AI agent bringing self-challenging logic to identity and cloud alert triageRapid triage agent (RTA) is Ruxie's latest power-up. It performs first-pass investigations and stress-tests its own reasoning to eliminate bias.
Threat intel | 17 min read
SynkLoader: when you throw in everything but the kitchen sinkDiscover a new malware family, SynkLoader. See how we reverse-engineered its phishing tactics to expose its attack chain.
Security operations | 4 min read
New Ruxie AI power-up: Phishing classification AI turns benign inbox noise into SOC focusRuxie's latest power-up, phishing classification, is an additive skill for our automated marketing engine; it automatically closes reported benign phishing.
Threat intel | 1 min read
Patch Tuesday: August 2026 (Expel’s version)August's Patch Tuesday is here, and it includes 398 CVEs, with three zero-days we recommend adding to the top of your priority list.